Dek: Google’s new google-cloud-developer bundle joins Skills, official-docs grounding and Cloud tooling for Codex, Claude Code and Antigravity. That can simplify a safer start, but it does not answer the harder production question: what exactly did the agent load, access and change?
Google Cloud’s new google-cloud-developer plugin is small in the way a well-packed emergency kit is small: it puts several things that are usually scattered across instructions, repositories and local configuration into one installable bundle. Its contents matter because the bundle is meant to help coding agents authenticate, reason about IAM, manage projects and work with gcloud—not just write code that happens to mention a cloud API.
Google announced the plugin on September 10 and says it follows the Agent Plugins specification, a vendor-neutral format for packaging Agent Skills and MCP servers. The company documents installation paths for Codex CLI, Claude Code and Antigravity. In its own onboarding example, the agent checks the environment, considers IAM practice and proposes a roadmap before it modifies resources. Those are promising defaults for a category that too often jumps from an eager prompt to a privileged shell.
The unresolved part is less glamorous: a package that brings documentation and tools closer to an agent also brings the path from suggestion to production closer. Teams should treat it as a deployable dependency with an identity and a change trail, not as a productivity add-on.
The useful part is the coupling
Cloud agents usually fail in the seams. A model may know a service name but not which project is active; a copied command may be technically valid but run under a human’s broad credentials; documentation may be stale by the time an incident begins. A hand-built setup can work, but it leaves each team to assemble prompts, MCP settings, shell wrappers and safety conventions on its own.
Google’s pitch is that related capabilities should travel together. The plugin bundles Cloud Skills with configuration for the Developer Knowledge MCP server, which Google says grounds an agent in current official developer documentation. The plugin’s scope includes authentication, authorization, project management and guardrails for gcloud commands. That is a more consequential package than a code-completion template.
For a developer starting a sandbox project, the bundle could remove real friction. The documented flow asks the agent to check prerequisites and surface a plan before creating or changing resources. A platform team can also begin from a shared baseline instead of maintaining a private folder of instructions that few people remember to update.
Google’s statements about reduced context use and easier management are vendor claims, though, not independent measurements of faster or safer delivery. Cross-client portability is similarly a design goal, not proof that every client will implement permissions, lifecycle behavior or auditing in exactly the same way.
Portability helps at the install boundary, not necessarily at the control boundary
The Agent Skills specification defines a portable directory structure centered on a SKILL.md file, with optional scripts, references and assets. That kind of common shape is useful: developers need fewer one-off wrappers when moving an agent workflow between supported environments.
But a common manifest does not make a Cloud workflow cloud-neutral. The useful operations here still depend on Google Cloud’s identities, projects, APIs, billing controls and command-line semantics. Nor does it ensure that a client will present a permission request, record an approval or expose a rollback path in the same way as another client.
| Area | Google’s packaged approach | Control a team still owns |
|---|---|---|
| Setup | Skills and MCP configuration travel together. | Pinning, review and rollback of the installed revision. |
| Knowledge | Official-docs grounding is configured in the bundle. | Record the documentation version or response used for a change. |
| Cloud actions | IAM-aware guidance and gcloud guardrails are part of the stated scope. |
Least-privilege credentials, scoped projects and human approval for writes. |
| Portability | A common plugin layout can reduce client-specific wiring. | Verify feature parity and audit logs in each actual agent harness. |
Source: Google Cloud’s launch post and the Agent Skills specification. “Control a team still owns” is AI News Fab analysis.
That distinction will matter most to U.S. enterprises with established identity, change-control and audit obligations. The plugin may make a first Cloud-agent pilot more approachable, but it cannot choose whether a contractor’s local session can touch production, whether a service account is limited to read-only discovery, or whether a destructive command requires a second human.
The audit gap is a concrete one
One public issue in Google’s skills repository makes the problem unusually clear. It notes that several facts are different: an update succeeded; an immutable revision exists; that revision became the registry default; and a particular long-lived agent actually loaded it. An agent can keep an older revision cached after a new default is published. The issue asks documentation to label runtime-loaded revision as unknown unless the loader provides evidence.
That is not evidence that the Cloud plugin is faulty. It is a useful warning against a familiar shortcut: confusing published configuration with observed runtime behavior. The same gap applies to documentation grounding. “Official” is valuable provenance, but an operator investigating an incident still needs to know which document or tool response influenced the agent’s action and when.
A pilot should be narrow enough to inspect
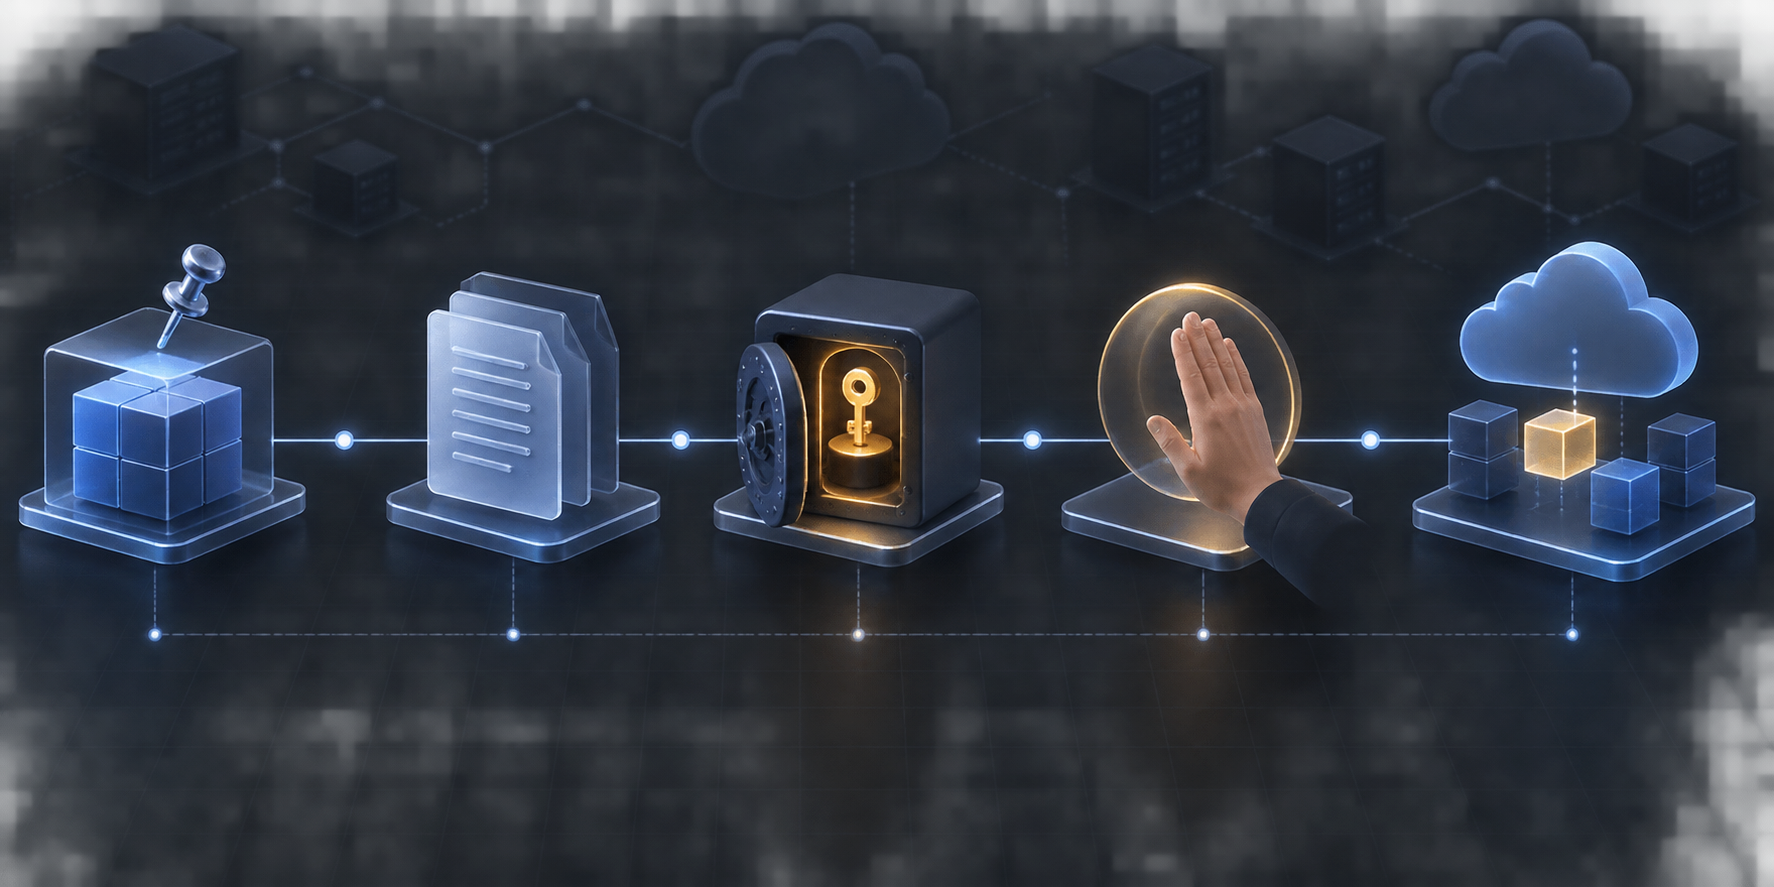
The sensible first deployment is not “give the agent our Cloud account.” It is one sandbox project, a disposable or narrowly scoped identity, read-only discovery by default and an explicit confirmation before any write. Capture the installed plugin revision; log the agent client version, active account, target project, documentation lookup, proposed commands and approval decision. Then compare intended versus resulting infrastructure state.
That has a cost. Teams that only wanted a faster way to generate boilerplate may decide the overhead is not worth it. They do not need a privileged Cloud plugin for a local refactor, a documentation summary or a unit-test task. The plugin makes the most sense when a workflow genuinely benefits from current Cloud context and controlled operational access.
The counterargument is strong: a documented, vendor-maintained starting point may be safer than thousands of improvised agent setups with copied credentials and unreviewed shell access. The answer is not to avoid packaged tooling. It is to demand evidence from it.
Google’s release moves cloud coding agents toward a more usable knowledge-and-action layer. The next competitive frontier may be less about which agent can compose a command and more about which environment can prove the full chain behind it: the package revision, the documentation context, the identity, the approval and the resulting change. For teams assessing AI-agent infrastructure, that trail is the product.
Related reading: AI News Fab coverage of AI-agent infrastructure